Cloud infrastructure and data center
Services

Cloud Infrastructure

NIRA helps federal agencies modernize mission-critical systems by designing, migrating, and operating secure cloud environments aligned with federal Cloud Smart guidance and Zero Trust principles.

What We Do

Full Lifecycle Cloud Services

NIRA's Cloud Infrastructure services cover the full lifecycle — from strategy through operations. Because NIRA also specializes in advanced research and development in cloud computing, semantic web, and AI, we design infrastructure that is ready to host next-generation analytics and AI capabilities from day one.

Cloud Strategy & Architecture

We work with CIOs, business owners, and security teams to define cloud strategies, reference architectures, and roadmaps that align with agency objectives, enterprise architectures, and federal Cloud Smart guidance.

Application & Data Migration

Our engineers plan and execute migrations of legacy applications and databases to commercial and government cloud environments, modernizing configurations while preserving mission functionality and data integrity.

Cloud-Native Modernization

Where appropriate, we re-platform and refactor systems into cloud-native services, microservices, and serverless patterns to improve elasticity, reliability, and long-term maintainability.

Infrastructure as Code & Automation

We implement infrastructure as code (IaC), CI/CD pipelines, and automated monitoring so agencies can deploy, update, and recover environments consistently and repeatably.

Operations, Optimization & FinOps

Our teams provide ongoing cloud operations support — capacity management, performance tuning, cost analysis, and optimization — so agencies get maximum value from their investments.

StoryAzure · AWS

From Replication to Readiness

Moving a federal system to the cloud is the easy part. Making it work there is the job.

Copying servers into the cloud is the easy part. A system is only migrated when the people who depend on it can do their jobs — securely, at full speed, from day one.

That's why NIRA treats every migration as a readiness exercise, not a replication exercise. We start by mapping how an application really works: who uses it, what it connects to, and what it quietly depends on. We move in controlled phases, rehearsing every step before production so that cutover day holds no surprises. And we don't hand a system back until its data has been verified and its performance measured under real load — because a database that restores is not the same as one that is ready for users.

One architecture, any cloud

Every environment we deliver follows the same shape, whether it runs on Azure or AWS. A secure edge sits in front: content delivery and web protection for public traffic, a secured gateway for partner connections, private access for agency staff. Behind it, the application tier — web portals, case and workflow systems, APIs — and the data tier it relies on live inside a defined security boundary, with controlled connections out to the systems they depend on: identity and directory services, agency systems and data feeds, and the agency's security operations center.

Each system runs in separate development, test, staging and production environments, so every change is proven before it reaches users. And two sets of controls span every tier: security and compliance — Zero Trust access, hardened images, continuous monitoring, vulnerability remediation, compliance evidence — and operations — configuration and change control, backup and rollback rehearsal, performance tuning and cost management.
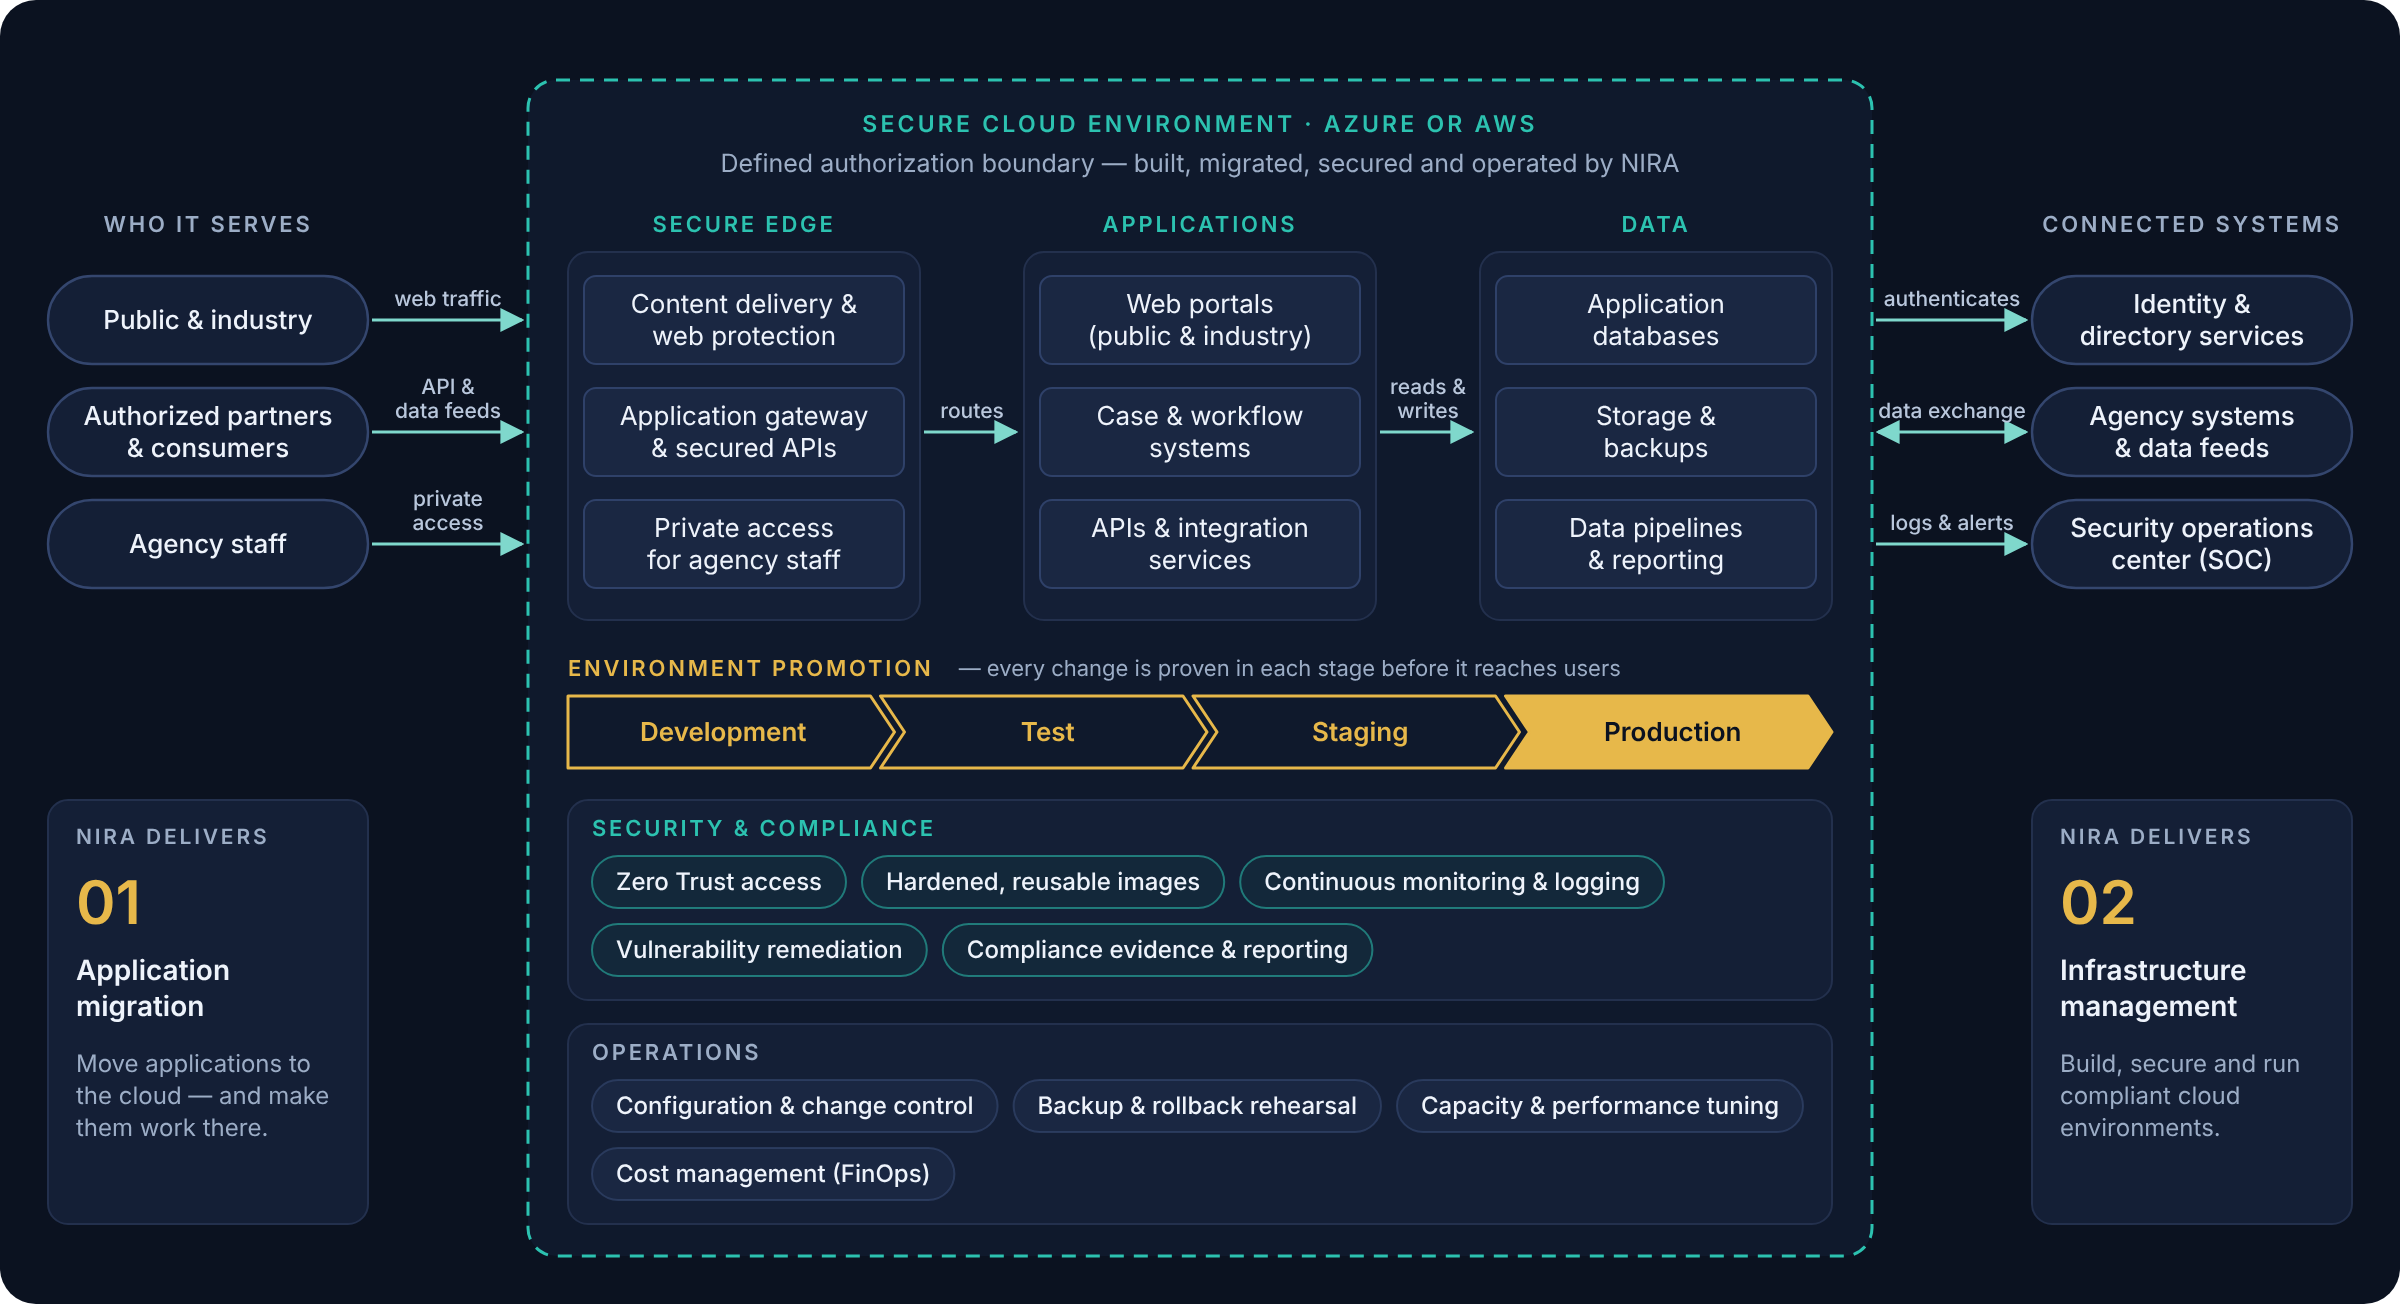
NIRA federal cloud reference architecture: public and industry users, authorized partners, and agency staff connect through a secure edge to application and data tiers inside a defined authorization boundary on Azure or AWS. Controlled connections link to identity services, agency systems, and the security operations center. Changes promote through development, test, staging, and production, with security, compliance, and operations controls spanning every tier.View full size
NIRA's federal cloud reference architecture — the same shape on Azure and AWS: a secure edge, application and data tiers inside a defined boundary, controlled connections to agency systems, and environment promotion with security and operations controls across every tier.

Because the shape is consistent, so is the work. We map an application onto it before the move, migrate it tier by tier, and then run it with the same playbook — building and hardening the environment, watching it continuously, keeping it compliant, and managing cloud spend so agencies see the value they were promised. Then we help them optimize what they have and modernize what comes next. The lessons from one program carry directly into the next.

Along the way, our engineers use AI to accelerate the routine work — scripts, tests, troubleshooting — while a person stays accountable for every change that reaches production.

This is the approach we have proven on live federal programs: migrating mission systems to Microsoft Azure for the U.S. Consumer Product Safety Commission (CPSC), and engineering and operating secure AWS environments for the Federal Aviation Administration (FAA). One partner for the full cloud lifecycle — on Azure and on AWS.

Secure & Compliant by Design

Security Is Foundational, Not an Afterthought

Security and compliance are foundational to our cloud work. We help agencies complete cloud migration while maturing cybersecurity and enabling AI-powered operations. Our ISO-aligned quality, service-management, and information-security practices reinforce disciplined, repeatable delivery for sensitive government workloads.

  • Align architectures with federal security directives, including Zero Trust strategies, continuous monitoring, and cloud-operations best practices
  • Implement role-based access control, encryption, logging, and auditing that support FISMA, privacy, and records-management requirements
  • Design environments that can safely host AI-enabled analytics and targeting systems without compromising data protection or mission integrity

Technologies & Standards

AWS GovCloudAzure GovCloudOracle CloudGCPFedRAMPZero TrustFISMACloud SmartIaC / TerraformCI/CDDocker / KubernetesDevSecOpsFinOpsAI / ML

Ready to modernize your cloud infrastructure?

We design phased migration plans that minimize downtime and risk.

Get in Touch